Blog
•
Compliance
PHP2Shell Showed What SOC 2 Was Never Built to Do


The week of October 19, 2026, the internet was ablaze with news of PHP2Shell, two critical vulnerabilities in PHP, which powers a sizable chunk of the internet. Every security team asked the same two questions: Where are we running PHP, and how fast can we patch it?
In this post, I’ll share a behind-the-scenes look at what our team did immediately following the disclosure of PHP2Shell. I’ll also talk about what this week revealed about the gap between passing an audit and staying secure.
What We Did
Around 23:56 on October 20, the Oneleet team used the platform’s Attack Surface Management (ASM) and Dependency Scanning features to collect a list of customers with PHP instances. This resulted in nearly 800 assets and more than 100 accounts being flagged.

Around 10:40, on October 21, our Security Program Managers (SPMs) reached out to each impacted customer with a note telling them what was happening and steps to mitigate.
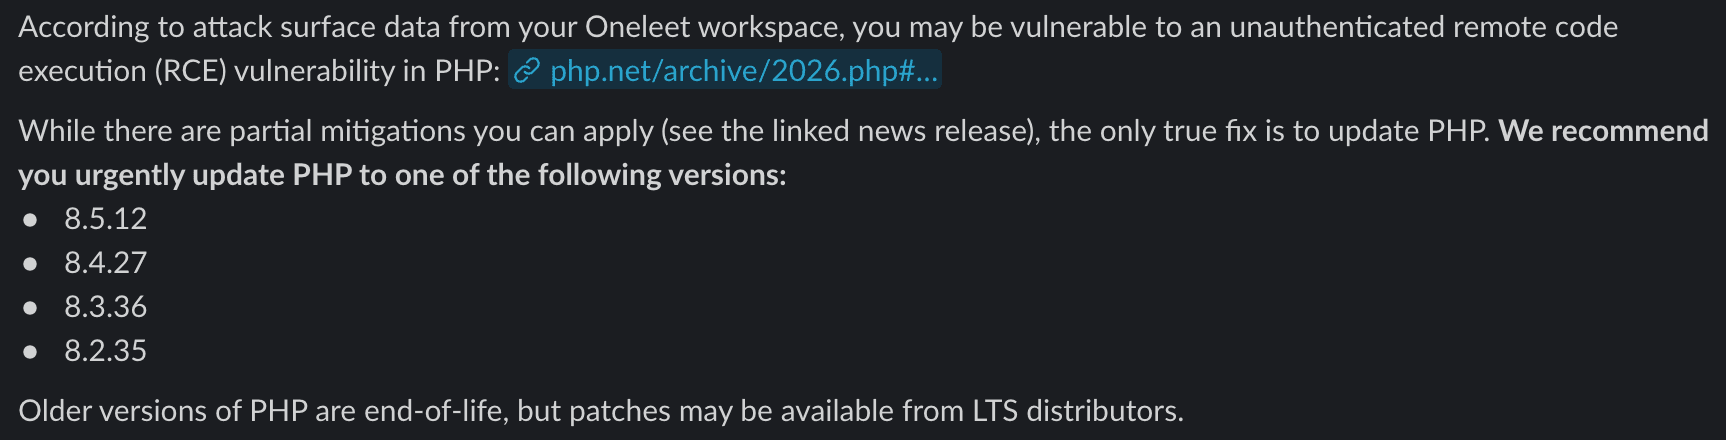
Due to our internationally diverse and passionate team, we were working on this even before major media picked up the story. Customers woke up to remediation advice and a calm, collected vCISO to help them navigate the fallout, instead of panicking alone from the breaking news headlines.
What We Found That Customers Didn’t Know They Had
A few of our customers wrote back to us, stating that they had no idea they had PHP instances in their environment. Turns out, these instances were hiding in plain sight as shadow IT. We were able to find them with our platform’s ASM and Dependency Scanning features, enabling our customers to take action.
You can’t patch what you don’t know you run. Knowing your attack surface is a security problem, and it’s one our platform is built to solve.
What Your Compliance Report Said About PHP2Shell
This week, every SOC 2 report ever issued said the exact same thing about PHP2Shell: nothing.
Compliance platforms can help you set up vulnerability management controls that pass an audit. A policy exists; a scanner ran.
Now, think of the company whose last scan finished on October 19. Their controls are in order, and their auditor signed off. The next day, they have an internet-facing PHP server nobody remembers deploying, a 9.2 CVSS vulnerability, and no one whose job is to tell them.
The audit did exactly what it was built to do. The problem is everything the audit was never built to do.
Checkbox Compliance vs. Security-Focused Compliance
A SOC 2 report shows that your controls worked during the audit window. But this week, the focus for everyone became am I secure right now? When compliance is disconnected from security, no one notices that gap. But when security is married to compliance, am I secure right now becomes a continuous question.
Here’s what this week looked like for companies with a checkbox compliance platform:
A scanner logged the CVE in a dashboard nobody will check until their next audit.
Their asset inventory, written for the auditor, didn’t include the PHP server nobody remembered deploying.
Their policy says critical issues get patched within [#] days, but no one is checking.
The week looked a bit different for companies with a security-focused compliance platform:
Someone emailed them the patched versions the day the vulnerability was disclosed.
Their ASM scan found PHP servers they didn’t know they had.
Someone actually checked that the vulnerabilities were patched.
We’ve said it before: Compliance is the floor. Helping customers stay secure between audits is the job of security-focused compliance vendors like Oneleet. Your SOC 2 report doesn’t protect a server running a 9.2 CVSS vulnerability, and your customers won’t care that it happened outside of your audit window.
None of what we did was heroic. We pulled a list of affected customers from tools we could see they had running, and we reached out to them with a fix. That’s because our job as a security-first compliance platform doesn’t stop once the audit is over. The real test is keeping our customers secure.
Preparing for the Next PHP2Shell
The next critical CVE is on the horizon. It might hit tomorrow, or next week, or in a month. Just like with PHP2Shell, your SOC 2 report won’t save you. That’s why it’s important to choose a vendor who cares about your security after the audit.
If you’re looking for a true security partner in the compliance space, book a demo with us. Our team will help you build a plan to get secure. Compliance will naturally follow.
" height="15.5px" id="S8Ax4rQUS" transform="translate(0.25 0.25)" width="15.5px"/></g></svg>)


