







Tell us about you
Share what you build, who you sell to and which badge you need, then connect your cloud, code and team tools. Oneleet tailors your security requirements to you.

Oneleet brings security and compliance into one platform.
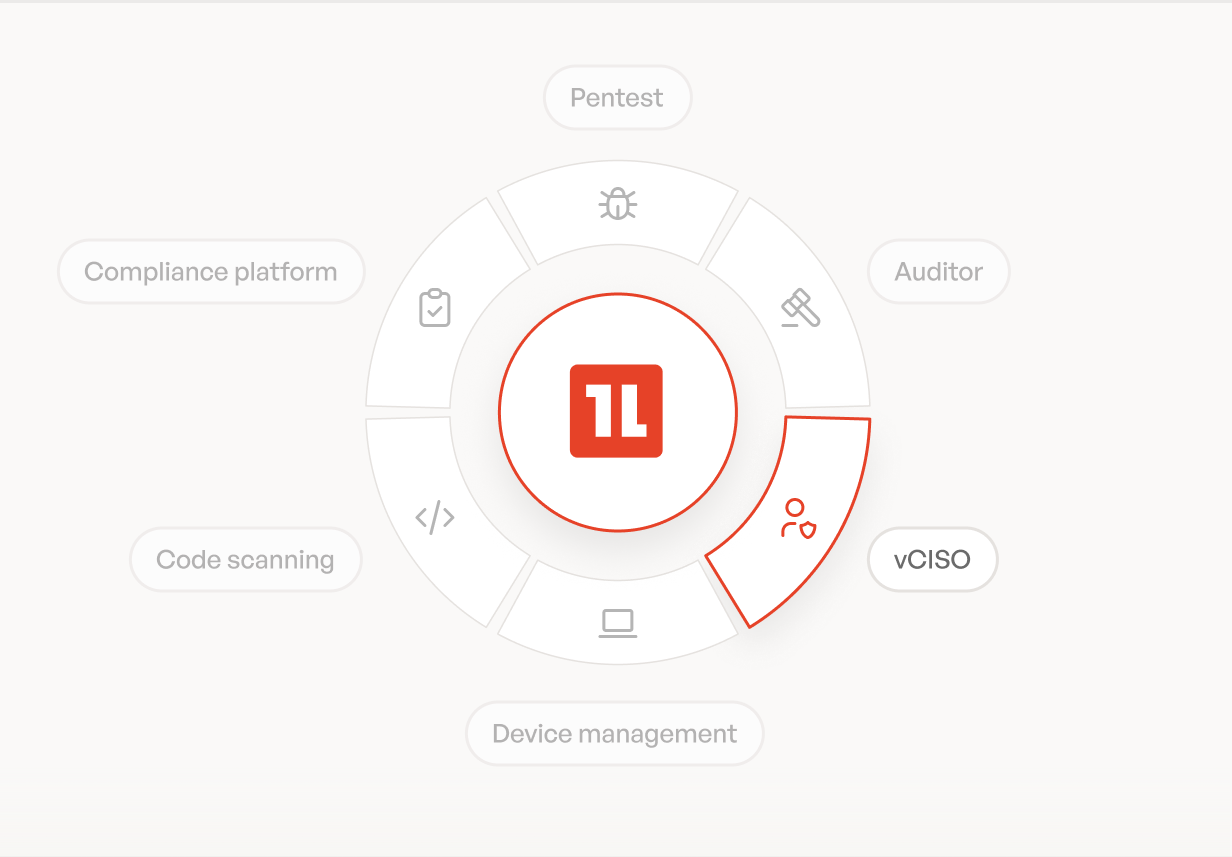
Human pentests, code scanning, device management, and a dedicated vCISO. One platform, one flat fee.
 4.9 / 5.0 (139)30-minute walkthrough



 Switched from another platform
“We chose Oneleet over Delve and Vanta”

“Consistently grateful we went with Oneleet. You and the team have been awesome.”

“If you actually want to be secure I'd recommend Oneleet.”





It doesn’t stop after the audit. Monitoring keeps running, so you stay green.
Share what you build, who you sell to and which badge you need, then connect your cloud, code and team tools. Oneleet tailors your security requirements to you.
Oneleet checks your stack against every requirement for your badge and turns each gap into a task. Most of them are automated.
Automation and Oneleet AI fix most gaps for you. Every fix is sent to a Oneleet expert for approval, so green means verified, not just marked done.
We review everything before the auditor does and work through their questions with you. The independent auditor signs your report, and your badge goes live on your Trust Center.
Most “compliance platforms” automate the paperwork and leave the real security to you.
Automated evidence, zero real testing. The certificate says “secure.” The pentest never happened.
Compliance in one tool, pentest in another, MDM somewhere else. Nothing talks to each other, so risks fall through the gaps, and the stitching falls on you.
The platform hands you a dashboard and wishes you luck the moment the hard questions start.
The quote covers the platform. The pentest, the audit, the vCISO each land later as their own invoice. By year two the one price you signed up for is five.

Everything the old way makes you juggle, Oneleet runs for you. One process, from kickoff to a signed, auditor-backed report.
| What you get |  Oneleet |  Compliance tools only |
|---|---|---|
| Dedicated security expert | vCISO in Slack | Customer success manager |
| Tailor-made program |  | Generic template |
| Manual pentest, OSCE testers | | Bought separately |
| Security stack included | |  |
| One control, many frameworks | |  |
| Auditor managed for you | | You find and manage it |
| Time to resolve security questionnaire | 30 min | 3 h |
| Manual compliance work | Our AI & team do the heavy lifting | Your team's second job |
| Expert on your sales calls | | |
| Vendors to manage | 1 | 6 |
| Audit-ready SOC 2 / ISO 27001 | | |
| Tested by hackers | | |
Oneleet | Compliance tools only |
|---|---|
 Dedicated security expert | |
vCISO in Slack | Customer success manager |
 Tailor-made program | |
 | Generic template |
 Manual pentest, OSCE testers | |
| Bought separately |
 Security stack included | |
| |
 One control, many frameworks | |
|  |
 Auditor managed for you | |
| You find and manage it |
 Time to resolve security questionnaire | |
30 min | 3 h |
 Manual compliance work | |
Our AI & team do the heavy lifting | Your team's second job |
 Expert on your sales calls | |
| |
 Vendors to manage | |
1 | 6 |
 Audit-ready SOC 2 / ISO 27001 | |
| |
 Tested by hackers | |
| |
You've been piecing together a pentest vendor, MDM, scanner, training tool, and consultant. Switch to one platform where everything connects seamlessly.
Continuous pentesting and monitoring, not a once-a-year checkup.

You built something worth protecting. Every customer gets a dedicated vCISO: ex-auditors and security engineers who know exactly what the auditor wants to hear, because they used to be the auditor.
 Mock audit before the real one.
 We negotiate with the auditor.
 Enterprise security reviews, handled.
Customer stories:DiligentCentralize
companies secured, from seed to enterprise.
teams migrated from Vanta, Drata and Secureframe.
vulnerabilities found and resolved.

“Ok so about 2 weeks into the SOC 2 process with Oneleet and we made the right choice.”

“If you're looking for security partners, there's no one better!”

“If you actually want to be secure I'd recommend Oneleet.”

“Left me excited about security. Not just the platform. Huge kudos.”

One control set maps across frameworks. Earn SOC 2 and you’re most of the way to the rest, with no duplicate work.
One control set maps across frameworks. Earn SOC 2 and you’re most of the way to the rest, with no duplicate work.
We test the systems you actually run, not a questionnaire. Every check shows what’s working, what isn’t, and which frameworks each gap touches.
Every result maps to the frameworks it belongs to. One gap can hold back several at once.
It prepares the fix, you approve it, and we retest. One verified fix counts toward every framework that needs it.
Some gaps need human judgment. Your Oneleet expert works through the details with you and verifies the result.
The same security work moves SOC 2, ISO 27001, GDPR, HIPAA, FedRAMP and ISO 42001 forward together. Explore the checks they share.
Oneleet adapts to your size, stack, and stage. The same real security, scoped to where you are.
Platform, pentest, vCISO and audit support included. Third-party fees quoted before you sign.
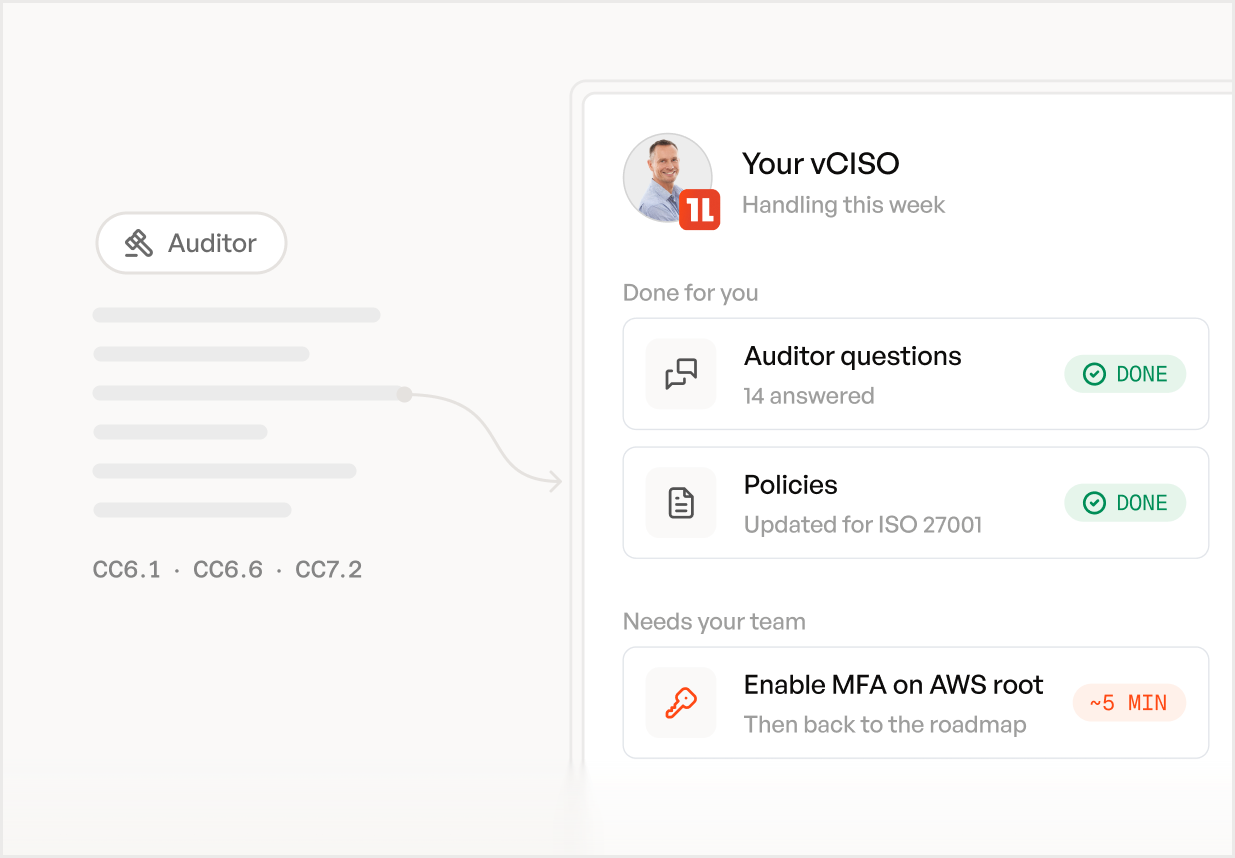
Your vCISO handles the auditor and turns questions into a to-do list. You keep shipping.
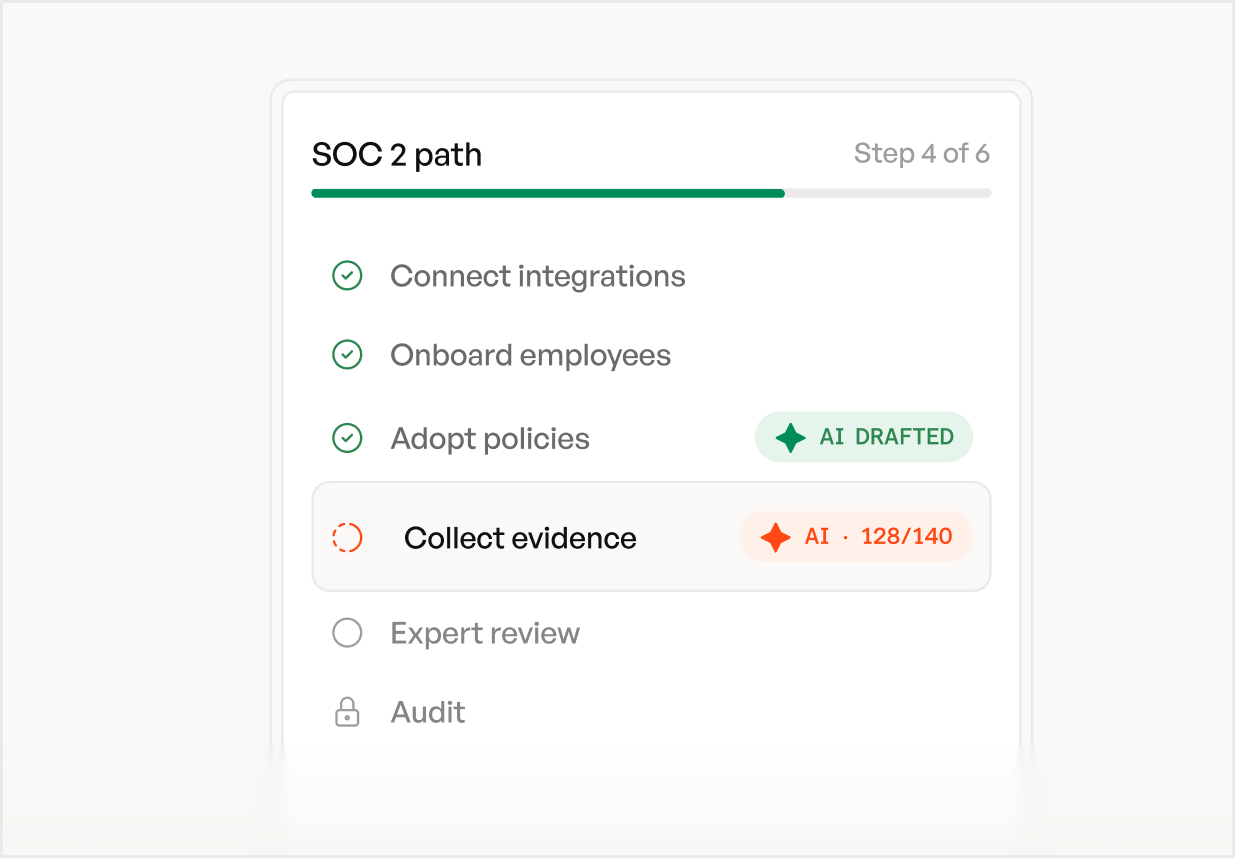
AI handles the manual work. A guided path per framework shows what's next.
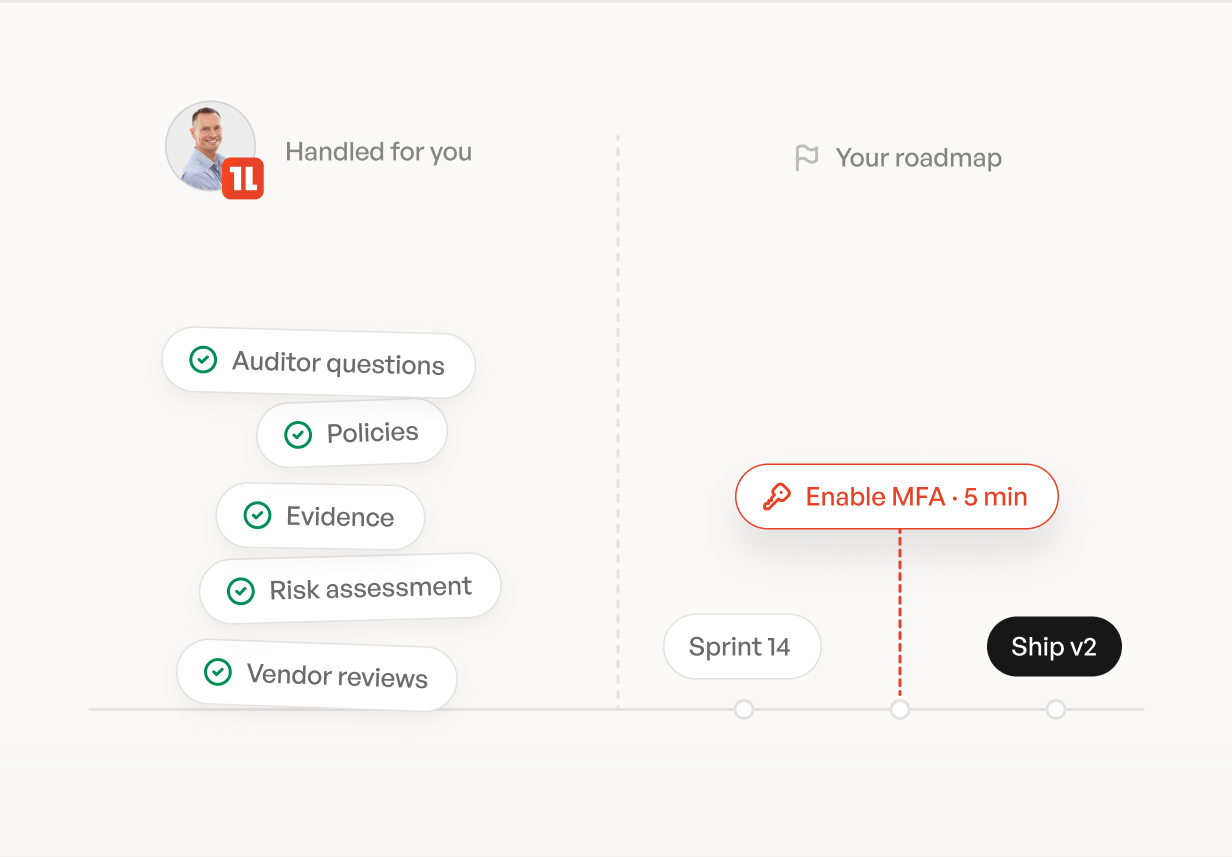
Your vCISO and the platform do the heavy lifting, so engineers stay on the roadmap.
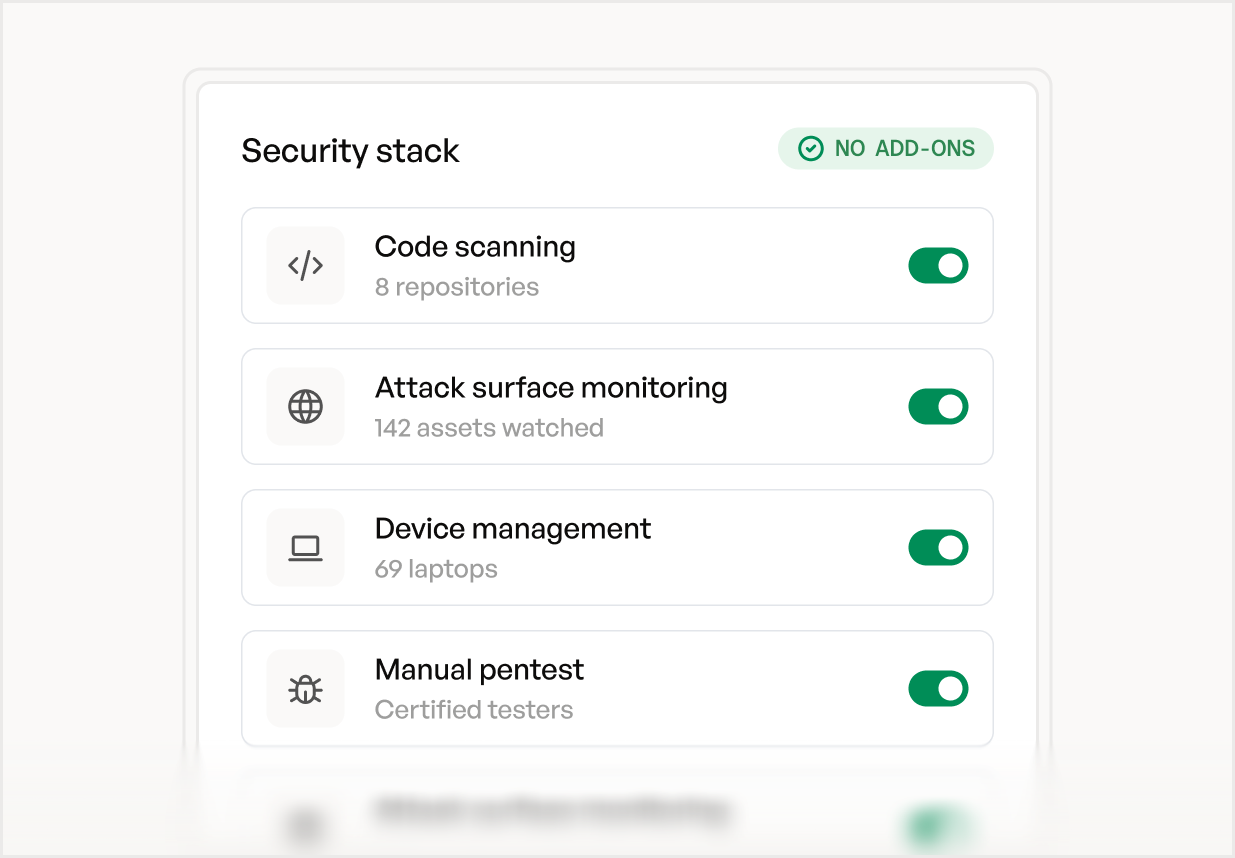
Code scanning, attack surface monitoring, devices and a manual pentest. No upsells.
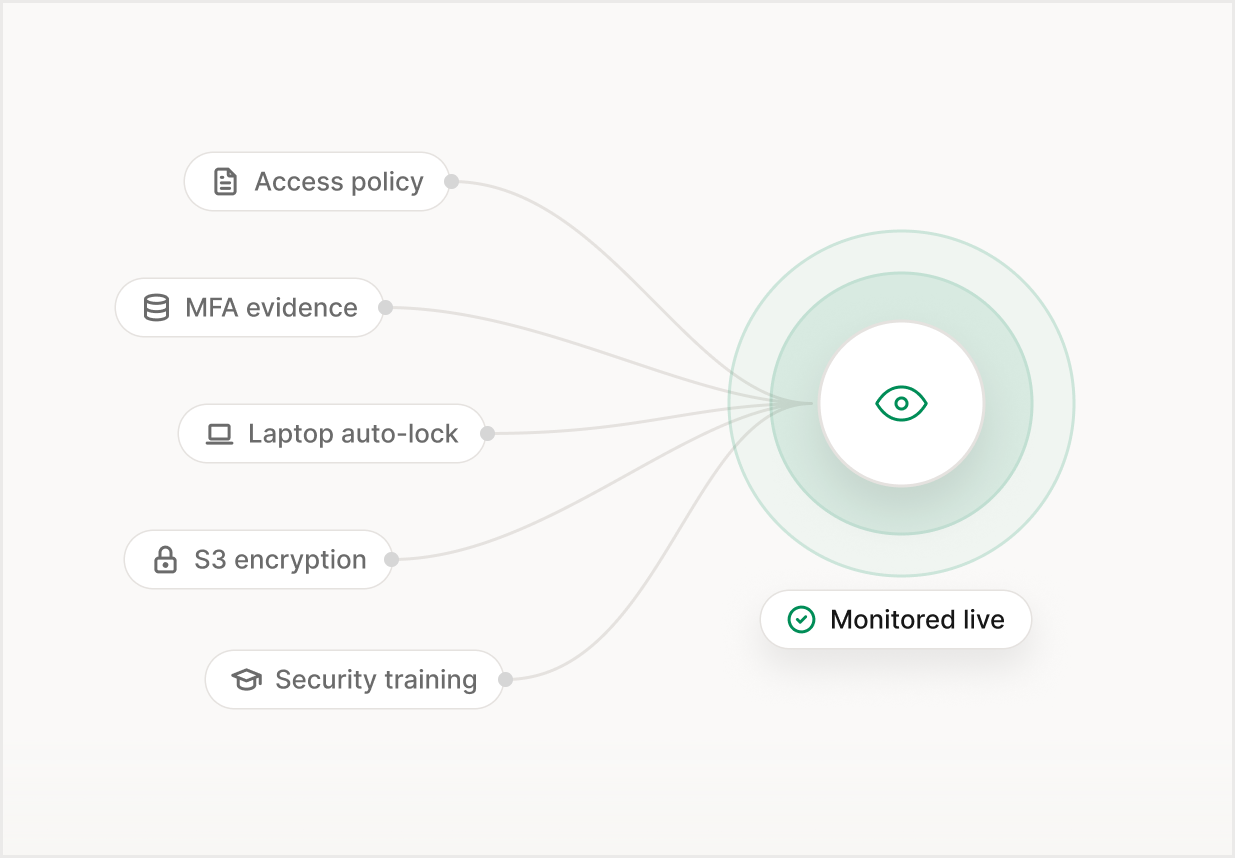
Every control, policy and piece of evidence in one place, monitored automatically.
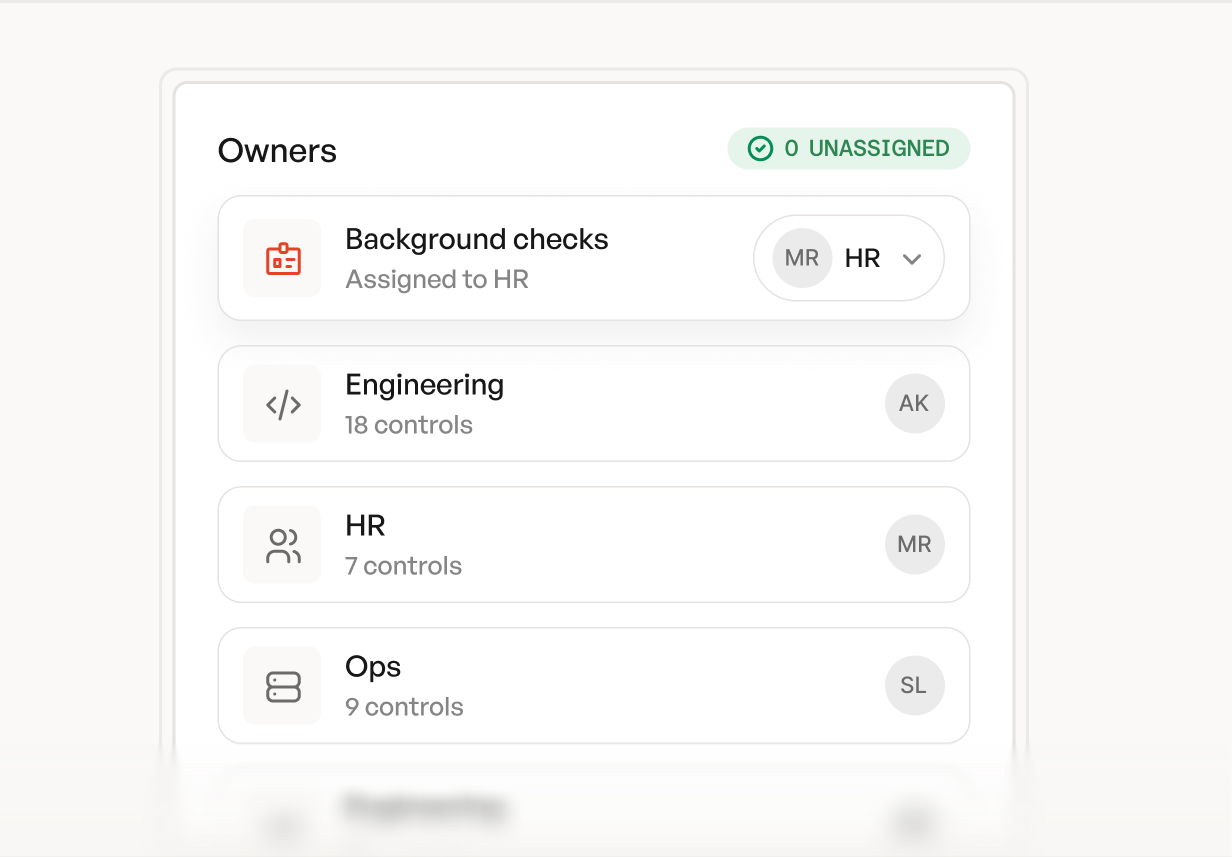
Assign each control to its owner across engineering, HR and ops. Nothing falls through.
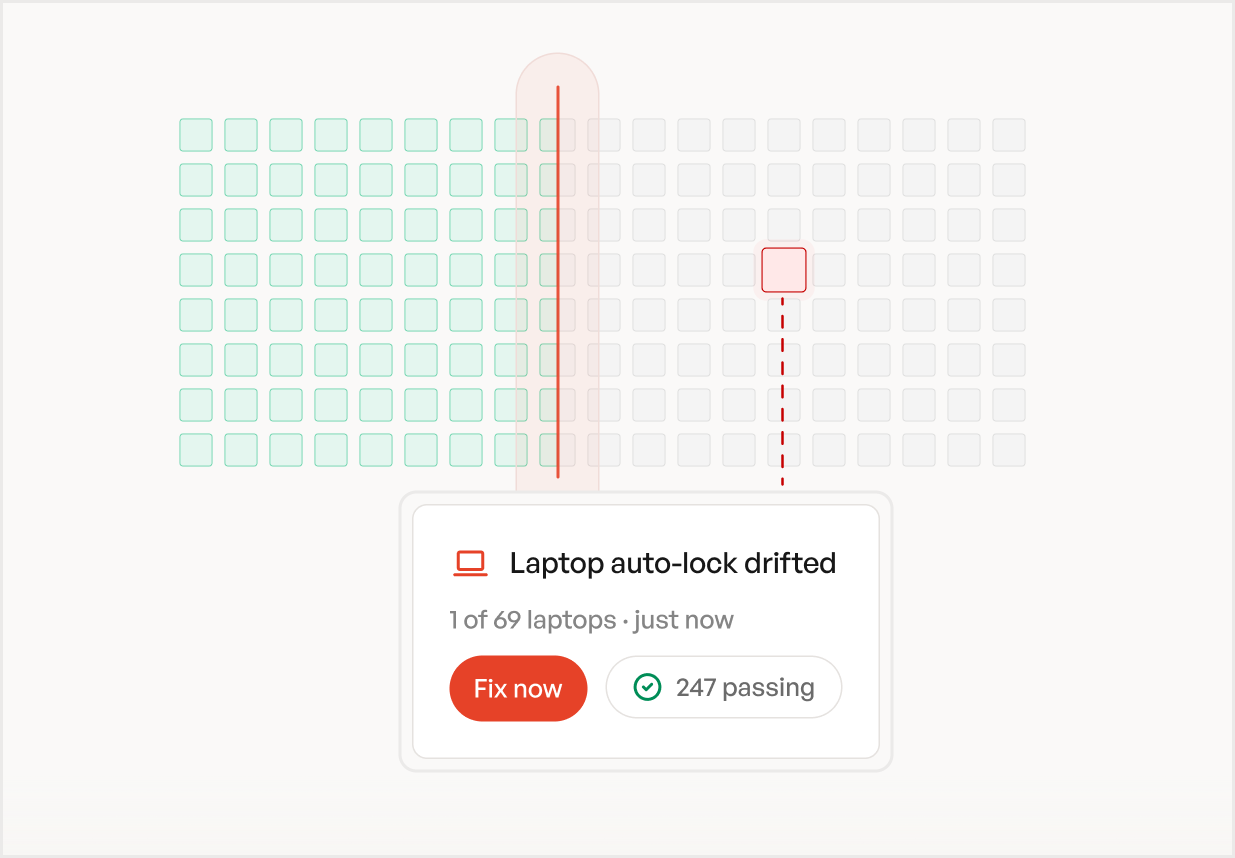
Monitors watch every control and flag drift right away. Fix one thing now, not fifty before the audit.
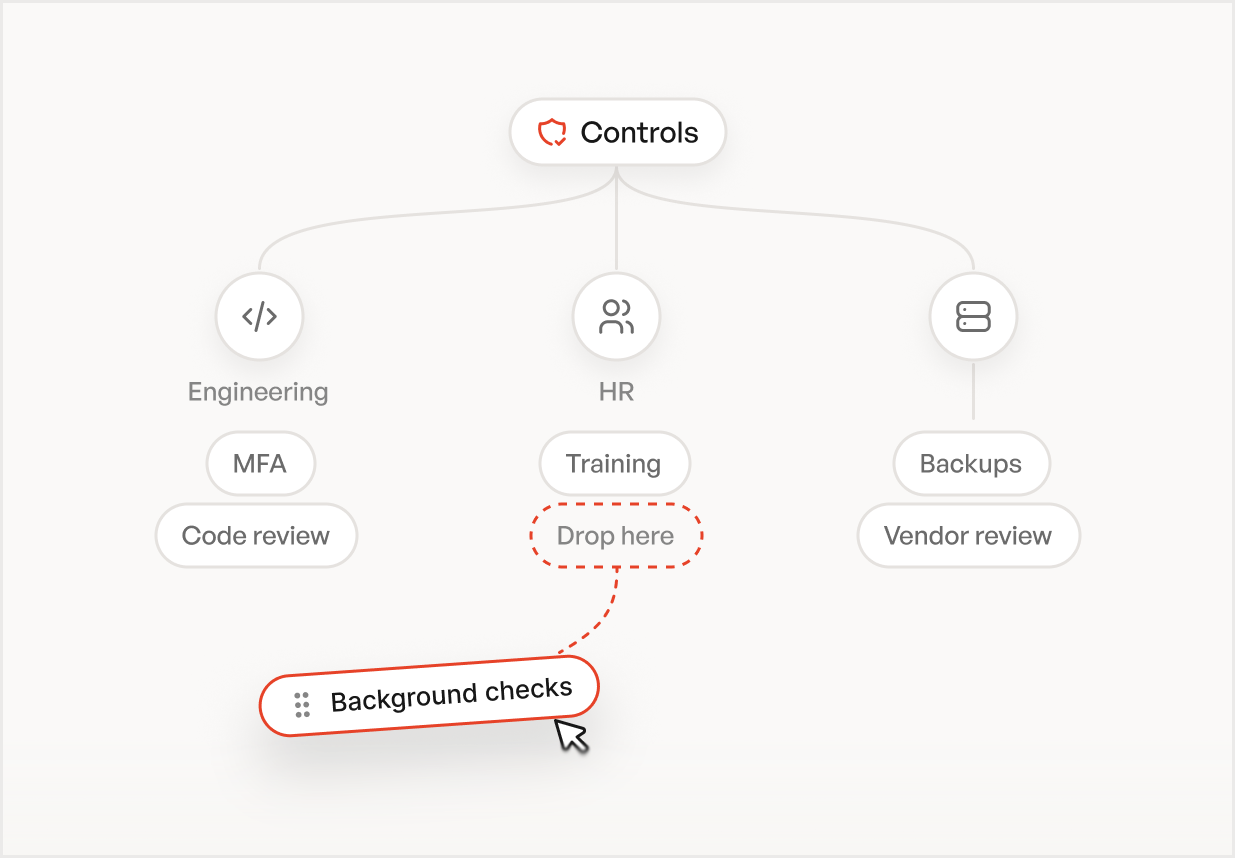
Add your own controls next to SOC 2, ISO 27001 and HIPAA. A program that fits you, not a checklist.
The pricing model the compliance industry should have started with. One flat fee, everything on the table, nothing waiting to ambush you at renewal.
See pricing OneleetSecurity included
 One flat fee.
Platform, pentest, and audit support included.
 IncludedEvery cost up front.
Third-party fees quoted before you sign.
IncludedEvery cost up front.We grow with you. We don't exploit you.
IncludedNo surprise invoices.Ever.
IncludedConnect your cloud, code, and workplace tools. Oneleet gathers evidence and checks for security gaps, so you don’t have to.


“Consistently grateful we went with Oneleet. You and the team have been awesome.”

They sell compliance automation: software that helps you collect evidence and pass an audit. Oneleet does that and the security itself: a real human pentest, code and dependency scanning, true device management, and a dedicated vCISO, all on one platform. With the others you assemble the rest yourself. With us it's included, connected, and one price.
Compliance paperwork alone doesn’t test your defenses. Oneleet includes the testing, scanning, monitoring, and security guidance that help you get compliant by actually getting secure.
Oneleet brings the work into one process instead of making you source and coordinate separate vendors. Your platform, pentest, and audit support are included, with third-party fees quoted before you sign.
Oneleet supports SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, and more. One control set maps across frameworks, so you can build on work you’ve already completed.
Oneleet works with teams moving from existing compliance platforms. Book a demo to walk through your current program and discuss a migration plan with the team.
Book a 30-minute demo and see exactly how Oneleet gets you compliant, secure, and ready to win your next enterprise deal. One platform, one price, no surprises.