
 Signed
Human + AI pentestwith every fix retested


Deal waiting on SOC 2? Your vCISO plans backward from your deadline, so you move fast without skipping the work your customer’s security team will check.
 4.9 / 5.030-minute walkthrough
Join 2,000+ startups building with Oneleet.




SOC 2 isn’t a certification. It’s a report, signed by an independent auditor, that shows your security controls work. Here’s what’s in one.

SOC 2 report
Your company · Your system
Everything below is in one flat fee, auditor included. No hourly consulting, no separate pentest invoice, and no surprise audit bill later.


Your vCISO confirms the report type, scope, and deadline, then plans preparation for your independent SOC 2 audit.
 Without Oneleet
 Unsure which SOC 2 report you need
 Evidence scattered across your tools
 Separate platform, pentest, and audit quotes
 Gaps discovered during the audit
 With Oneleet
 Report type and scope agreed at kickoff
 Evidence collected and reviewed in one place
 One flat fee for your agreed program
 A mock audit before the independent audit
The platform pulls evidence from your tools. Your vCISO reviews every item, so moving fast doesn’t mean getting it wrong.
 Evidence collection
 Continuous monitoring
 Policy templates
 Security questionnaires
 Device agent
 Trust Center
 One control, many frameworks

Evidence collection
Collects evidence from your tools to support SOC 2 audit preparation.
Oneleet platform
 Pulling access logs from Google WorkspaceChecking branch protection on 14 GitHub reposReading disk encryption on 42 laptopsExporting CloudTrail settings from AWS
 186 of 190 evidence items collected.
 4 need a person: your vCISO has them this week.
Continuous monitoring
Tracks controls and flags changes as your team prepares for SOC 2.
Oneleet platform
Re-testing 216 controls against your stackComparing device settings to policyWatching new repos and cloud accountsFlagging drift since the last check215 of 216 controls still passing.
Laptop auto-lock drifted on 1 device. Fix sent to the owner.
Policies
Drafts policies from your stack for vCISO review and your approval.
Oneleet platform
Reading your stack and team sizeDrafting 12 policies from templatesRemoving controls that do not applySending drafts to your vCISO for review12 policies drafted and reviewed.
3 wait for your sign-off before the audit.
Security questionnaires
Drafts customer answers from your policies while you work toward your report.
Oneleet platform
Reading a 230-question customer questionnaireMatching questions to your controlsDrafting answers from your policiesFlagging what needs a human answer214 of 230 answers drafted from your policies.
16 flagged for your vCISO to answer.
Audit readiness depends on your scope and starting point. You’ll know your full timeline, including the audit and any observation period, on day one.
Your vCISO joins your SlackDay 0
Share your customer’s requirements and deadline. Your vCISO plans the preparation work.
 A plan built from your deadline
Scoping call1–3 days
Agree the report type, systems, and controls in scope before collecting evidence.
Report type and scope agreed
Human + AI pentest1 week
Human pentesters test your application alongside preparation, then retest your team’s fixes.
Findings reviewed, fixes retested
Get your controls in place1–4 weeks
Connect tools, approve policies, and implement changes. Your vCISO reviews the evidence.
Controls and evidence prepared for review
Mock audit
Your vCISO and audit team check readiness and flag gaps before the independent audit.
A readiness check before the audit
Real audit
You engage the independent CPA firm directly. It audits and issues the report; Oneleet coordinates requests.
An independently issued SOC 2 report
Your vCISO guides preparation, pentesters retest fixes, and an independent CPA firm issues your SOC 2 report.
Your pentest team
Your human + AI pentest finds issues. Pentesters turn findings into tasks and retest fixes.
Pentest fixes
2 of 3 verified

Admin page open to members
GET /admin/users
 Verified

Any invoice readable by its ID
GET /invoices/1043
Verified
No rate limit on login
POST /auth/login
 Retest queued
Pentester
OneleetRetested after your fix. Still blocked.
Your dedicated vCISO
Your vCISO confirms scope, reviews evidence, and answers questions on Slack or calls.
Your audit, managed
We check your controls before the auditor does, handle their requests, and help your team respond with clear evidence.
See your SOC 2 report type, timeline, and cost before you commit.
Book Demo“That call left me *excited* about security. Not just the platform. Huge kudos.”

“@BryanOnel86 cares about their customers more than any provider ive ever seen”

“Our most recent Fortune 500 prospect wouldn't move forward until we had ISO 27001.”

“Talking to Bryan Onel about the Oneleet process felt a lot more personal and straightforward.”

“i’m such a happy @oneleet customer too (twice! gumloop and now understudy)”

“I love @oneleet and I love the team at Oneleet”

“Oneleet made this easy. They didn't show up with a checklist and tell us to comply.”

“Big thanks to the team at Oneleet for supporting us, and spending over 20 hours inside our production app and API for the pentest.”

“Thank you to Oneleet for their availability and professionalism throughout”

“On a Saturday, Samuel jumped on with us and spent hours making sure we got there. A deal was on the line and they treated it like it was theirs too.”

“SOC 2 Type II with Oneleet gave us the single pane of glass to prove at the organizational level what we'd already built into the product”

“Oneleet ran the program, Prescient Security did our controls examination, and we spent three months in the observation phase with an independent pentest along the way.”

“We did it with Oneleet. I wanted someone who would find real problems, not generate a checklist.”

“we chose OneLeet over Delve and Vanta.”

“- logs into our @oneleet control monitor dashboard - ensures timely review + merge of vulns - replies promptly to auditor requests”

“OneLeet is one of the best companies.”

“consistently hearing the best things about @oneleet”

“Glad we went with @oneleet when we got @skyvernai enterprise ready.”

“Consistently grateful we went with oneleet. You and the team have been awesome”

“if you actually want to be secure I'd recommend Oneleet”

“Ok so about 2 weeks into the SOC 2 process with @oneleet and we made the right choice.”

“@BryanOnel86 was the only vendor who expressed a genuine interest in security, not just speed”

“But we chose integrity, simple pricing model, expert guidance that kept me in check. AND They sure did.”

“We just moved our SOC 2 program to Oneleet.”

“We recently completed a full penetration test with Oneleet alongside our ISO 27001 implementation, with focused testing of the Co-Pilot for Marking® pipeline.”

“We are SOC 2 Type II certified with Oneleet, which reflects how we've built from day one.”

“Samuel Beyeler from their team spent hours with us on a Saturday just to make sure we'd make it. We closed the deal :)”

“That’s why we worked with Oneleet to get SOC 2 certified.”

“But Oneleet (and specifically Carter, our vCISO) made it easy and way more manageable than expected.”

“Their platform integrated directly with our cloud infrastructure and started automating evidence collection from day one.”

“They really feel like they are going above SOC 2. Doesn't feel like checking boxes like others did.”

“We also went with Oneleet based mostly on the vibe of integrity.”

“it was clear after talking to oneleet there is no legitimate way to get soc 2 done in in 3 weeks due to the observation period.”

“Thank you @oneleet and @avimakesrobots for getting this through the line!”

“After 3 months of observation, an independent pentest, and a controls audit by Prescient Security with @Oneleet.”

“I'm glad we're working with @oneleet 🙏”

Original post
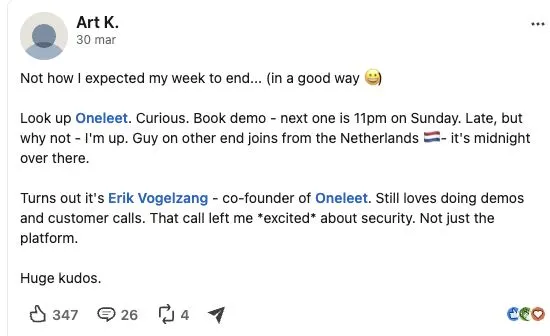
Art K
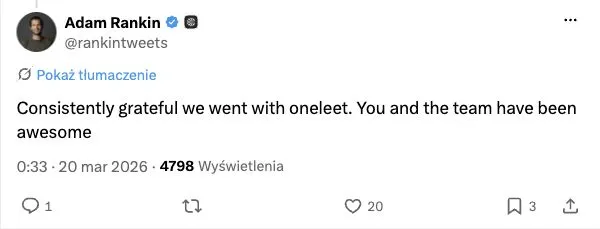
Adam Rankin
Brandon Veiseh
Brian Sierakowski
Jessica Collier, PhD
Daniel Wigh
Scott Motte
Nalin Semwal
Albert Lam
Luis Manrique
Amit Biswas
Jeremy Hindle
Ram Venkataraman
Andrew McGlathery
Dr. James Lambert
Ingemar Rask
Johannes Dancker
Jonathan Kopnick
Luigi Pedace
Marie
Michael Fester
Michelle Ann Gitlitz
Nils Howland
Oskar Klingberg
Peter F.
Ryan Underwood
Saif Mahmud
Shikhar Bhushan
Yannick Boerner
Soohyun Bae
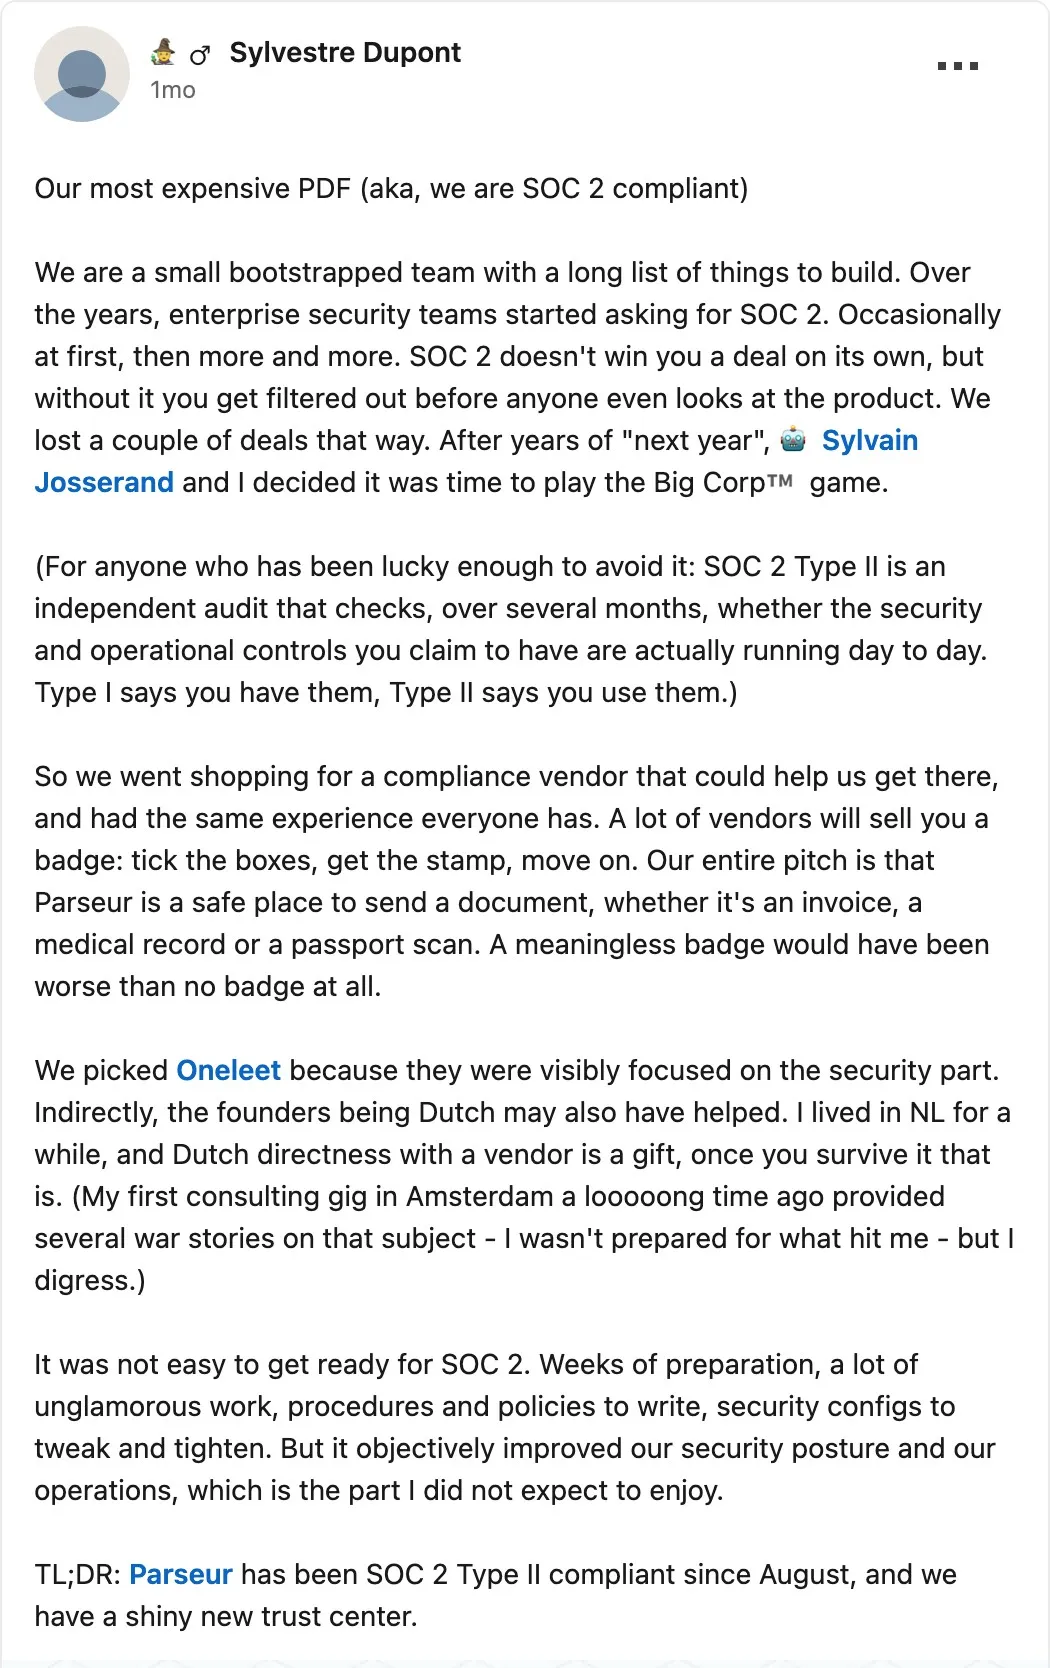
Sylvestre Dupont
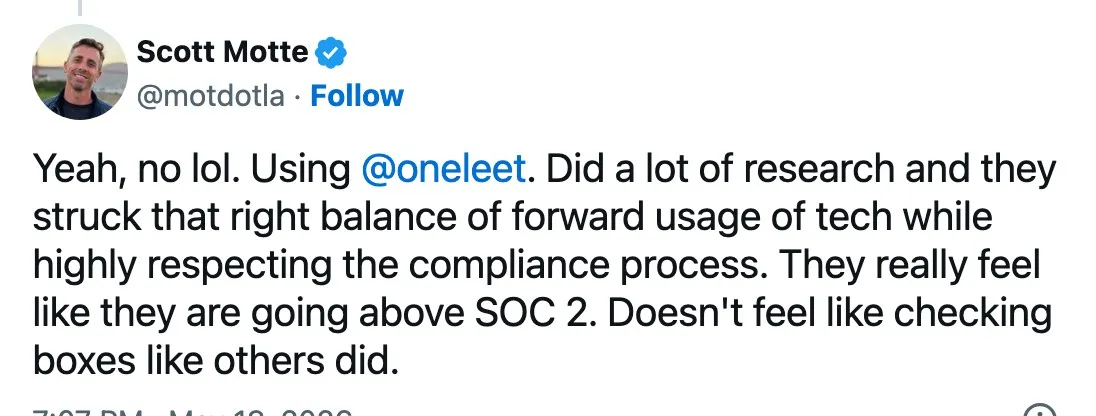
Scott Motte
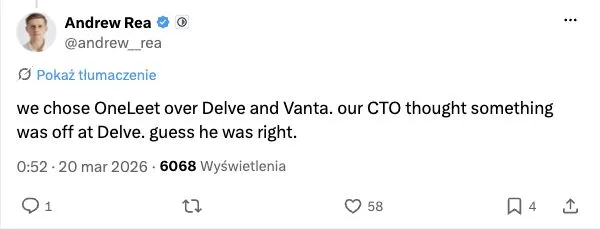
Andrew Rea
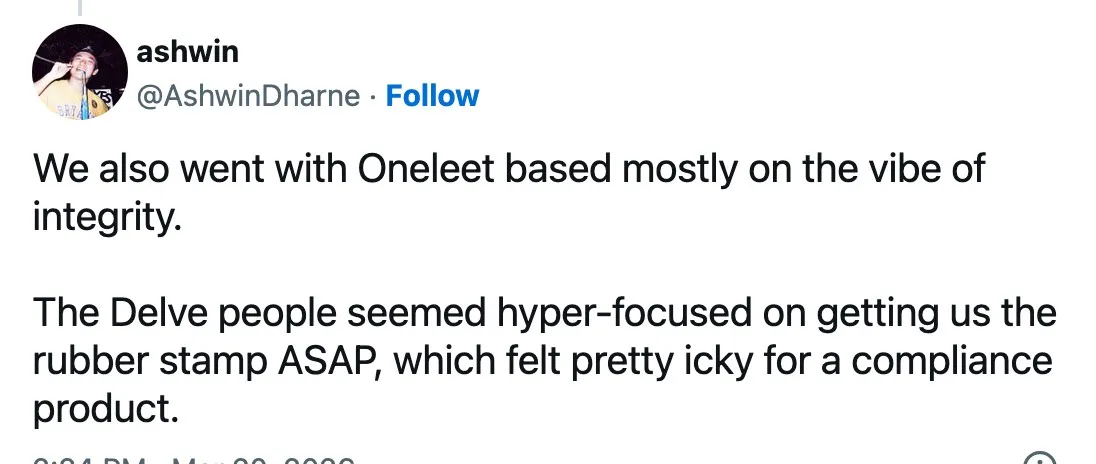
ashwin
claire vo
Cooper Newby
Jeet
Kiet
Neil Bhammar
s2.dev
Suchintan Singh
Tim Suchanek
“Consistently grateful we went with oneleet. You and the team have been awesome”


“SOC 2 certification” is a common way to describe completing a SOC 2 audit. What you get is a SOC 2 report, where an independent CPA firm checks your security controls and signs a report your customers can read.
Start with the report your customer needs and your target date. Your vCISO helps agree the report type and scope, then guides controls, policies, and evidence collection. The program includes a human + AI pentest and a mock audit before the independent CPA firm performs the audit and issues your SOC 2 report.
Your SOC 2 certification price is one flat fee for the agreed scope, covering the platform, dedicated vCISO, human + AI pentest with retests, and independent audit. We review your requirements and quote the scope and price upfront. Your team’s time to implement changes is also part of planning the total cost.
Confirm the report your customer requires, agree on the scope early, and assign owners for the work. Plan for 1–4 weeks to audit readiness, depending on your starting point and team availability. Report delivery also depends on independent audit scheduling, and a Type 2 report requires an observation period. Your vCISO helps build a realistic plan around those stages.
A Type 1 report evaluates the design of controls at a point in time. Type 2 also evaluates how those controls operate over a period. Start with what your customer requires. Your vCISO helps you choose the report type and plan preparation; a Type 2 observation period is separate from the time needed to become audit-ready.
An independent, licensed CPA firm performs the SOC 2 audit and issues the report under AICPA standards. You engage that firm directly. Oneleet helps prepare the controls and evidence and coordinates audit requests. The independent audit fee is included within the agreed scope of your Oneleet program.
Confirm the required report type, systems in scope, criteria, and reporting date with your customer before you start. Your vCISO uses those requirements to plan preparation for the independent audit. Acceptance depends on the customer’s review and requirements, so no provider can promise that every customer will accept every report.
Compare the full scope of each quote: platform access, readiness guidance, pentesting and retests, audit fees, and the work your own team must do. A low platform price may cover only one part of that work. Oneleet quotes one flat fee for the agreed program so you can see the included services before deciding.
Discuss your report type, deadline, and SOC 2 certification cost in a 30-minute demo.
Bring your requirements and target date.
Review the report type, scope, and next steps.
See the agreed scope and upfront price.


 Overview


 To-do


 Connected


 0 critical